Every business holding personal data in Rwanda must register
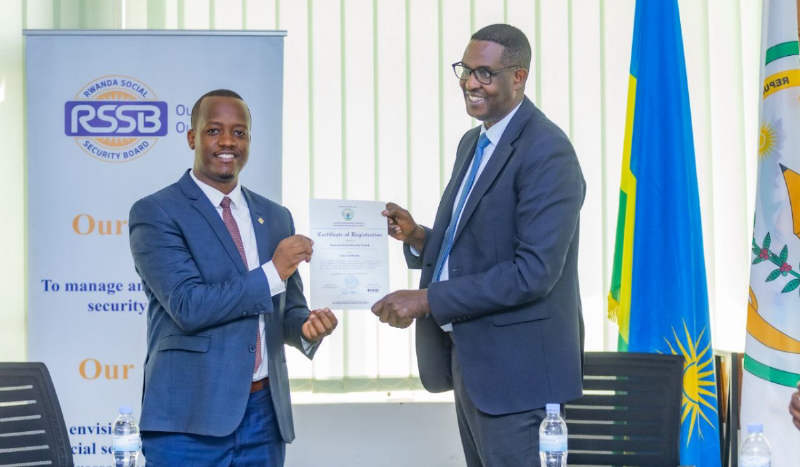
Law n° 058/2021 of October 13, 2021 relating to the protection of personal data and privacy was published in the Official Gazette on October 15, 2021. Article 29 requires every data controller and data processor to register with the National Cyber Security Authority. Article 67 gave existing businesses two years to comply, and that period ended in October 2023. Data controller registration in Rwanda is no longer something to keep on the back burner.
Who must register
A controller decides why and how personal data is processed, and a processor handles it for the controller. A school is the controller of its pupils’ records, and the company hosting its fee-payment system is a processor.
Article 2 reaches beyond Rwanda’s borders. The law applies to a controller or processor established in Rwanda, and to one based abroad that processes the data of people located in Rwanda. Under Article 39, a foreign controller or processor must appoint a representative in Rwanda in writing.
The application
Article 30 requires the applicant’s identity and a single point of contact, any representative’s details, a description of the data and the people it concerns, the purposes of processing and the recipients, the countries the data will go to, and the risks and the measures against them. The form cannot be completed off the top of your head. It needs a data inventory first.
Under Article 31, the Authority issues the certificate within 30 working days. The duty continues afterwards. Article 32 requires changes to be reported within 15 working days, Article 33 allows renewal up to 45 working days before expiry, and Article 35 allows cancellation for false information or non-compliance after 15 working days’ notice.
Data must stay in Rwanda
Article 50 requires personal data to be stored in Rwanda unless the registration certificate authorises storage abroad. This is the point most businesses miss. A company that keeps payroll on a group server in Nairobi, or customer records with a cloud provider in Europe, needs that written on its certificate.
Transfers abroad are governed by Article 48. The grounds include the Authority’s authorisation on proof of safeguards, the data subject’s consent, performance of a contract, public interest, legal claims and vital interests. Article 49 requires a written contract setting out each party’s role.
Data protection officers and breaches
Article 40 requires a data protection officer where processing is carried out by a public or private body, where core activities involve large-scale systematic monitoring, or where they involve large-scale processing of sensitive data or criminal records. A group may share one officer if each establishment can reach that person easily.
Under Article 43, the controller notifies the Authority within 48 hours of becoming aware of a breach, and a processor notifies its controller within the same period. Article 44 requires a detailed report within 72 hours, and Article 45 requires notice to the people affected where they face high risk. A group plan written around the 72-hour European deadline will drop the ball in Rwanda.
The penalties
Operating without a certificate, or with an expired one, is an administrative fault under Article 53, as is failing to appoint a data protection officer or to notify a breach. The fine is RWF 2 million to 5 million for an individual and 1% of global turnover in the preceding financial year for a corporate body. Article 54 allows an appeal to the competent court.
The criminal penalties are heavier. Selling personal data carries five to seven years in prison and a fine of RWF 12 million to 15 million under Article 59, and unlawful processing of sensitive data carries seven to ten years under Article 60. A corporate body convicted of an offence pays 5% of annual turnover under Article 62, and the court may close the business under Article 63.
A game plan
A business not yet registered should build its data inventory and file, by the book, since the application is a declaration to a regulator.
A registered business should compare its certificate with the systems it uses today and report new ones within 15 working days.
A foreign company with customers or staff in Rwanda should appoint its Article 39 representative.
A business using automated tools to assess people should read our commentary on the right not to be subject to automated decisions.
The bottom line is simple. Registration is mandatory, the transition period is long over, and the certificate must match how the business actually handles data.